
13 Best WordPress Security Plugins (2026) Tested & Compared
An in-depth comparison of the best security plugins for WordPress.

Last updated: November 10, 2026 by The WP Umbrella Team.
“Best” depends entirely on how many sites you run.
If you own one website, the best security plugin usually means a firewall plus malware scanning inside WordPress: something that blocks bad traffic, flags infected files, and locks down your login page.
If you manage client sites, “best” means something else. It means vulnerability monitoring, safe updates, backups, rollback, and one place to prove the work to clients, without bolting a heavy plugin onto every site you touch.
That distinction runs through this whole comparison, because most real WordPress compromises come from predictable gaps: outdated plugins, weak credentials, missed alerts, and no fast recovery path. Close those and you have shut the doors attackers actually use. Below are 13 options tested and ranked, with a table first so you can pick by your setup, then a short buying guide and a full review of each.
WordPress Security Plugins at a Glance
Every option below is scored on the four factors that decide fit: firewall type, malware scanning, starting price, and whether it suits a single site or a whole portfolio. Skim the table, then read the short version underneath for the quick picks.
| Plugin | Type | Best for | Firewall | Malware scan | Price (from) |
|---|---|---|---|---|---|
| WP Umbrella | Platform | Agencies and freelancers managing client sites | Yes (add-on, virtual patching + WAF) | Yes (add-on, remote) | €1.99 / site / mo |
| Wordfence | In-WP plugin | Single-site WordPress firewall and scanning | Yes (application WAF) | Yes (local) | Free; $149 / yr |
| Solid Security | In-WP plugin | Single-site login hardening | Login and brute-force only | File-change detection | ~$99 / yr * |
| Sucuri | Platform (cloud WAF) | Hands-off malware cleanup | Yes (cloud WAF) | Yes (remote) | $229 / yr |
| All-In-One Security | In-WP plugin | A free option for beginners | Yes (basic) | File scanning (basic) | Free; $69.99 / yr |
| WPScan | In-WP plugin / API | Developers and vulnerability monitoring | No | No (vulnerability database) | Free; Enterprise (custom) |
| BulletProof Security | In-WP plugin | A one-time payment for unlimited sites | Yes (.htaccess firewall) | Yes (MScan) | $69.95 one-time |
| SecuPress | In-WP plugin | The best single-site standalone plugin | Yes (application) | Yes (local) | Free; €60 / yr |
| All-in-One Login | In-WP plugin | Login-page hardening and 2FA | Login protection | No | Free; $29 / yr |
| MalCare | Platform | Cloud malware scanning with cleanup | Yes (cloud) | Yes (remote) | Free; $99 / yr |
| Jetpack Security | In-WP plugin | Automattic-ecosystem backups and scanning | Basic | Yes (remote) | ~$25 / mo |
| WP Cerber | In-WP plugin (self-hosted) | Single-site anti-spam and login security | Yes (application) | Yes (local) | Free; $29 / qtr |
| Cloudflare | Network WAF / CDN | A network firewall in front of any site | Yes (managed ruleset on Pro+) | No | Free; $20 / mo (Pro) |
* Solid Security (formerly iThemes) is now Kadence Security as of 2026, on sliding-scale pricing; see its section below. Vendor links are nofollow. Prices verified against each vendor’s own pricing page in August 2026.
Short version: if you manage client sites, WP Umbrella is the strongest all-round pick, because it covers what actually creates risk at scale (vulnerability monitoring, safe updates, backups, rollback, virtual patching, and client reporting) from one place. If you run a single site and want a plugin you install and forget, SecuPress or Wordfence are the better fit. If you want cleanup handled for you, look at Sucuri or MalCare.
How We Tested, and Why Trust WP Umbrella
We build WordPress maintenance infrastructure. Our platform monitors more than 100,000 WordPress sites, and over 10,000 of them run our Security add-on. That vantage matters here: we do not only see which vulnerabilities get disclosed, we see which ones actually get attacked, across thousands of live sites at once. Our own IP abuse list is built in real time from that traffic, something a single-site plugin cannot replicate.
For this comparison we scored each option on the things that decide real outcomes: firewall type (application-level versus network), how malware scanning runs (locally in PHP or remotely), vulnerability monitoring, update and backup coverage, performance impact, pricing transparency, and fit by number of sites. Every price was verified against the vendor’s own pricing page in August 2026.
We deliberately did not rank plugins by their WordPress.org star ratings. Ratings mix old and new versions, get gamed, and tell you little about protection quality. Capability and fit tell you more.
Performance carried real weight in the scoring, because a security plugin that slows a site down gets disabled, and a disabled plugin protects nothing. Application-level scanners and firewalls that run in PHP carry the most overhead; remote and network-level approaches carry the least. Where a product runs its heavy work matters as much as what that work does.
Do I Need a WordPress Security Plugin?
Security plugins are helpful, but they are not mandatory for every website. A poorly coded one can slow your site down or pile on features you never use.
WordPress does not require a plugin to be hardened, and many protections can be applied by hand. The catch is that hardening a site well is close to a full-time job, and for most owners it is better left to people who do it every day. So if there is money at stake on your site, whether revenue, bookings, or customer data, you should run one.
No CMS is completely safe, WordPress included. The cost of getting security wrong is rarely just the hack itself: it is the downtime while the site is offline, the hours spent cleaning up, the sales lost during the outage, and the trust you forfeit with visitors who hit a warning screen.
For a personal blog, that is a nuisance. For a business site, or a client’s site you are responsible for, it is real money and real reputation. That asymmetry is why a modest monthly cost usually pays for itself the first time it prevents one incident.
The State of WordPress Security in 2026
The threat picture is getting busier, not calmer. According to Patchstack’s State of WordPress Security 2025, 7,966 new WordPress vulnerabilities were disclosed in 2024, up 34% year over year; 96% of them were in plugins and 4% in themes, and 33% were still unpatched on the day they went public. Wordfence blocked more than 55 billion password attacks in 2024 alone, and Sucuri’s 2024 malware research recorded 1,176,701 infected websites. The pattern is clear: outdated third-party code is where sites get breached, so monitoring and fast patching matter more than any single feature.
What to Look For, and How to Choose
Start with the two questions that decide everything else: how many sites are you responsible for, and how much of the work do you want to do yourself?
If you run one site, you want an application-level firewall, malware scanning, and login hardening in a single plugin. Budget matters less than ease of use, since you configure it once.
If you manage client sites, per-site plugins become a maintenance burden of their own. You want vulnerability monitoring, safe updates with rollback, reliable backups, and reporting across the whole portfolio, from one dashboard. A platform beats a stack of plugins here.
Cloud WAF versus application firewall
This is the distinction most comparisons skip, and it changes what a plugin can actually protect.
An application-level firewall runs inside WordPress, as a plugin executing in PHP. It sees WordPress context (users, requests, plugin behavior), so it can make smart decisions. The trade-off: it uses your server’s resources, and it only acts once traffic has already reached your server. Wordfence and All-In-One Security work this way.
A cloud or network firewall runs before traffic reaches your site, at the DNS or proxy layer. It filters attacks upstream with no load on your server, but it cannot see inside WordPress, and it needs a DNS change to set up. Sucuri and Cloudflare work this way. Worth knowing: Cloudflare’s free plan only includes basic managed rules; the full WAF managed ruleset, including OWASP core protections, needs the Pro plan ($20 per month) or higher.
A third layer, virtual patching, sits between the two. It blocks the specific known exploit for a vulnerable plugin at runtime, before the official fix ships or before you have had time to apply it. WP Umbrella (through Patchstack) does this, which is why a well-monitored, well-patched site can stay safe even during the 33% window when a disclosed bug has no patch yet.
Run through this quick checklist before you decide: your budget, your number of sites, your technical skill, whether you need hands-on malware cleanup, and whether you need client-facing reports. Your answers point straight at the shortlist below.
What a good security layer should cover
Whatever you choose, the strongest options deliver a similar core set of protections. Use this as a shortlist test:
- Active monitoring of known vulnerabilities and security threats
- Malware and file scanning, ideally run off your server
- Blocklist and IP-abuse monitoring
- Security hardening: login limits, user-enumeration blocks, file-editor lockdown
- A firewall, at the application or network level
- Brute-force and login protection
- A clear recovery path: reliable backups and one-click restore
A plugin that covers most of these is worth shortlisting. One that only hardens the login page, or only scans for malware, is a single layer, and you will need to pair it with something else.
Do you need more than one?
Often, yes, and that is not a failure of any single product. A sensible stack combines a network firewall in front of the site (Cloudflare), an application-level layer inside WordPress (a plugin or a platform like WP Umbrella), and dependable backups underneath both. The network layer stops volumetric and generic attacks, the application layer catches what is specific to WordPress, and backups get you back online if something still slips through. Do not skip that last part. A firewall lowers the odds of a breach, but a tested backup and a fast restore are what turn an incident into an hour of downtime instead of a lost site.
The 13 Best WordPress Security Plugins in 2026
Here is the full breakdown, starting with the best fit for people who manage client sites, then moving through the strongest single-site plugins, the cloud services, and the specialist login layers.
1. WP Umbrella
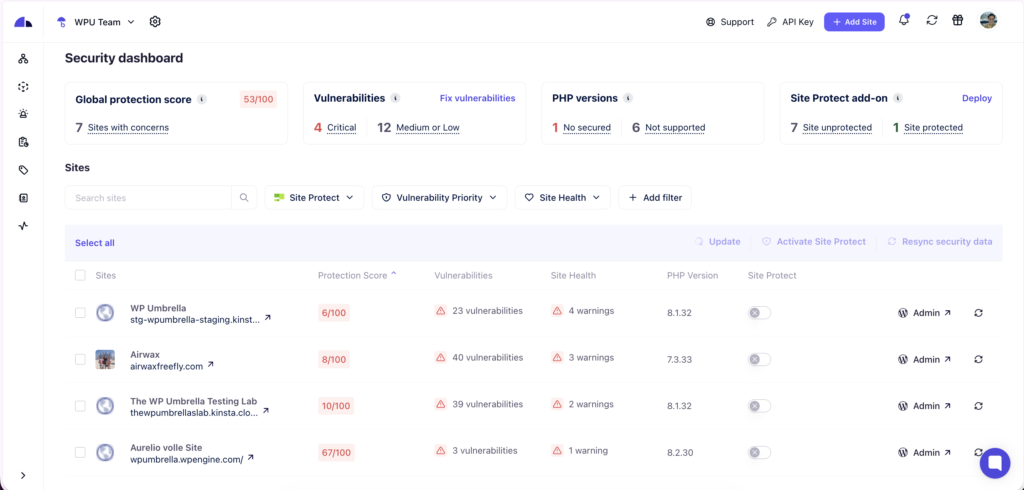
Best for: agencies and freelancers who manage client sites and want security folded into maintenance.
WP Umbrella is a WordPress management platform first, and it covers a large part of your security stack from the same place you run updates, backups, monitoring, and client reporting. It is not an in-WP plugin bolted onto every site; it is the infrastructure that replaces plugins like Wordfence, Sucuri, and Solid Security with a Patchstack-powered suite that does not weigh your sites down.
Here is how the two layers split.
The base platform (€1.99 per site per month) includes continuous vulnerability monitoring every six hours against the Patchstack database, with one-click fixing updates; per-site security hardening toggles (including login rate limiting and uploads-folder protection); two-factor authentication on the WordPress login, switched on per site, with your one-click access from the dashboard still working; encrypted, GDPR-compliant backups on a daily, weekly, or monthly schedule, stored on European servers for up to 50 days and restorable in a few clicks; safe bulk updates with visual regression checks and automatic rollback; uptime, PHP-error, and performance monitoring; site-health warnings; and white-label reports to prove the value of your care plans.
This split is what makes it different from a plugin. A per-site plugin protects one site and stops there. When you manage a portfolio, you also have to prove the work: show a client that updates ran, backups completed, and vulnerabilities were caught and fixed. WP Umbrella turns that into scheduled, branded reports pulled from the same dashboard where the security lives, so the value of your care plan is visible without extra effort.
The optional Security add-on (€2 per site per month) turns on the protection layer: firewall and virtual patching through Patchstack, which blocks known exploits at runtime before a fix exists; WP Umbrella’s own network-learned IP abuse list, built in real time from attacks across thousands of sites; a security-driven activity log that runs eight attack-detection checks (brute-force, new or hidden admin accounts, sign-ins from new locations, file integrity, critical settings changes, mass content deletion, and .htaccess changes), each alert carrying its evidence; and a daily remote malware scanner (released July 16, 2026) that runs on our infrastructure with zero load on your site and checks core, plugins, themes, uploads, crons, and supply-chain code. Malware cleanup and database scans are available on demand.
Since October 2026 there is also a one-off Security Audit, at €30 per site with no subscription, for any site connected to WP Umbrella. If the site was compromised, the report tells you what happened, when, how the attacker got in, and what to do first. If it was not, you get proof that the site is clean, written so you can forward it to your client. You order it from the site’s Security tab and it is generally ready within an hour. Cleanup is an optional extra at €180.
The platform also connects to AI assistants. The WP Umbrella MCP server, included in every plan, lets you ask Claude, ChatGPT, or Cursor which of your sites have open vulnerabilities or failed backups, without opening the dashboard.
Pricing: €1.99 per site per month for the base platform, plus €2 per site per month for the Security add-on when you want the firewall and scanner. The Security Audit is a separate one-off purchase. That works out to roughly €24 per site per year for the base, and about €48 all-in with security, well below Wordfence (from $149 per year) or Sucuri (from $229 per year), while also covering updates, backups, monitoring, and reporting those plugins do not touch.
Pros
- One platform for security, updates, backups, monitoring, and client reporting
- Virtual patching and remote scanning with no measurable performance hit
- Network-learned IP blocklist built from attacks across the whole network
- Hardening and two-factor authentication included in the base price
- Transparent, flat per-site pricing with no seat charges
Cons
- Built for people managing sites; overkill if you only own one personal blog
- Malware cleanup is on demand rather than fully automatic
Start your free trial (no credit card required), or read how WordPress care plans package this work.
2. Wordfence
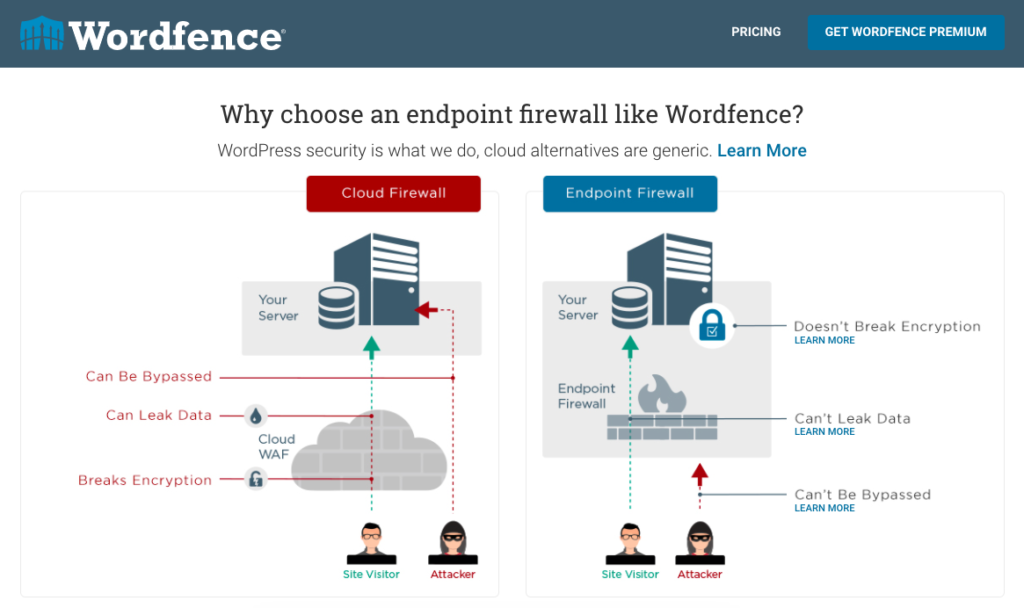
Best for: a single site owner who wants a WordPress-level firewall and malware scanning inside WordPress.
Wordfence is one of the most popular WordPress security plugins, and for good reason. It combines a strong web application firewall, a malware scanner that checks core files, themes, and plugins for backdoors and code injection, leaked-password protection, and two-factor authentication. The ability to watch traffic patterns and hack attempts in detail is a real draw for hands-on owners. Because the firewall runs inside WordPress rather than at the DNS layer, it cannot be sidestepped by routing traffic around it, and the free tier already delivers meaningful protection before you pay anything.
Key features:
- Application-level web application firewall (WAF)
- Malware scanner for core, theme, and plugin files
- Leaked-password protection and two-factor authentication
- Live traffic and hack-attempt monitoring
Pricing: free version available; Premium from $149 per year, up to the Wordfence Response incident-response plan at $1,250 per year.
Pros
- One of the most complete feature sets of any security plugin
- A genuine WAF that runs inside WordPress and cannot be bypassed at the DNS layer
- Free tier is useful on its own
Cons
- Runs in PHP, so it can be resource-heavy and slow sites on shared hosting
- Relatively expensive at the premium tiers
See our full Wordfence versus WP Umbrella comparison if you manage more than a handful of sites.
3. Solid Security (now Kadence Security)

Best for: single-site login hardening from a well-known plugin lineage.
Solid Security, formerly iThemes Security, has long been one of the most installed security plugins, built around login protection: brute-force lockouts, file-change detection, 404 detection, database backups, and security-key management. It hardens the parts of WordPress attackers probe first. It also includes an “away mode” that hides the dashboard during hours you never log in, a small but effective way to shrink the attack window on a site you rarely touch.
As of 2026, Solid Security has been consolidated under Kadence Security by StellarWP and Liquid Web. Its pricing runs on a sliding annual scale rather than fixed tiers, so check the current terms and product name before you buy.
Key features:
- Brute-force protection and login lockouts
- File-change detection and 404-scan lockouts
- Two-factor authentication and strong-password enforcement
- Scheduled database backups and security-key management
Pricing: historically a sliding annual scale, from roughly $99 per year for a single site up to around $499 per year at the top of the range. A free version covers the basics.
Pros
- Broad set of login and hardening controls
- Established, widely used codebase
- Does not noticeably slow sites down
Cons
- Now consolidated under Kadence Security, so check the current product name and terms
- Focused on hardening rather than deep malware scanning
4. Sucuri Security
Best for: owners who want malware cleanup and a cloud firewall handled for them.
Where most tools on this list ask you to fix an infection yourself, Sucuri does it for you. Now owned by GoDaddy, it routes your traffic through a cloud firewall before it reaches your host, filtering malicious requests upstream, while its team handles malware removal, blocklist removal, and SEO-spam cleanup on your behalf. If you would rather pay experts than fix an infection yourself, this is the model. It suits busy owners and ecommerce sites where downtime is expensive and hands-on cleanup is not an option, though you should budget for the DNS change the cloud proxy requires and expect the strongest response times on the higher tiers.
Key features:
- Cloud-based web application firewall (WAF)
- Server-side malware scanning and removal by experts
- Blocklist monitoring and removal requests
- SEO-spam and defacement cleanup
Pricing: Basic $229 per year, Pro $339 per year, and Business $549 per year, each for one site, with a 30-day money-back guarantee.
Pros
- Strong cloud-based firewall with no load on your server
- Malware cleanup done by security professionals
- Comprehensive monitoring across the platform
Cons
- Expensive, especially across multiple sites
- Cloud proxy setup adds a DNS step, and can affect performance
- Uptime monitoring is less reliable than dedicated tools
Compare it directly in our Sucuri versus WP Umbrella breakdown.
5. All-In-One Security (AIOS)

Best for: a capable, free starting point for beginners.
If you want to learn WordPress security while you harden a site, All-In-One WP Security & Firewall is one of the friendliest ways in, and one of the most feature-packed free plugins available. It grades your site’s security strength, groups features into Basic, Intermediate, and Advanced tiers so you can go as deep as you like, and focuses on user-account security, login protection, and file and database safeguards. The visual security dashboard is genuinely good for learning what to fix, and the tiered approach means a beginner can start with the Basic settings and grow into the Advanced ones without switching plugins.
Key features:
- Login lockdown and user-account security
- .htaccess and wp-config backup and restore
- Visual security-strength grading
- Blocklist tool and file-integrity checks
Pricing: free core plugin; Premium from $69.99 per year (rising to around $349 per year for unlimited sites).
Pros
- Free and friendly for beginners
- Clear, visual way of presenting security data
- Solid login and account protections
Cons
- Fewer advanced features than premium-first plugins
- Limited support on the free tier
6. WPScan
Best for: developers, agencies, and pentesters who want authoritative vulnerability data.
WPScan, acquired by Automattic in November 2021, scans WordPress installations against what is widely regarded as the most comprehensive WordPress vulnerability database. It is built for security professionals, system administrators, and penetration testers, and it delivers instant alerts, CVSS risk scores, API access, and Slack or HTTP webhooks. It is a vulnerability scanner, not a firewall or malware remover, so it pairs well with a protection layer rather than replacing one.
Key features:
- The most comprehensive WordPress vulnerability database
- Instant email alerts and CVSS risk scores
- API access with Slack and HTTP webhooks
- Regularly updated API endpoints
Pricing: free plan capped at 25 API requests per day; Enterprise pricing on request, scaled to your monthly API volume.
Pros
- The most comprehensive vulnerability database for WordPress
- Real-time alerting with risk scoring and webhooks
Cons
- No firewall and no malware cleanup; monitoring only
- Enterprise pricing is not published, so you have to request a quote
7. BulletProof Security

Best for: one-time pricing across unlimited sites.
Actively developed and unusually feature-dense, BulletProof Security packs more into one plugin than most, including an MScan malware scanner, login and security monitoring, database prefix changing, idle-session logout, a plugin firewall, upload anti-exploit protection, anti-spam, and detailed security logging. It works well as an all-around plugin, and it handles database backups and login security in one package. Much of its protection is built on .htaccess-level rules, which act before requests reach WordPress, though that same approach is what makes the setup feel technical.
Key features:
- MScan malware scanner for files and database
- Plugin firewall and upload anti-exploit protection
- Database prefix changer and monitoring
- Idle-session logout and detailed security logging
Pricing: free version available; the Pro version is $69.95 one-time for an unlimited number of websites, with a 30-day money-back guarantee.
Pros
- Comprehensive feature set for a one-time price
- Frequently updated by the developer
- Unlimited-site license is a strong value for portfolios
Cons
- The interface is dense and dated
- Setup can be intimidating for beginners
8. SecuPress
Best for: the best single-site standalone security plugin, especially if interface quality matters to you.
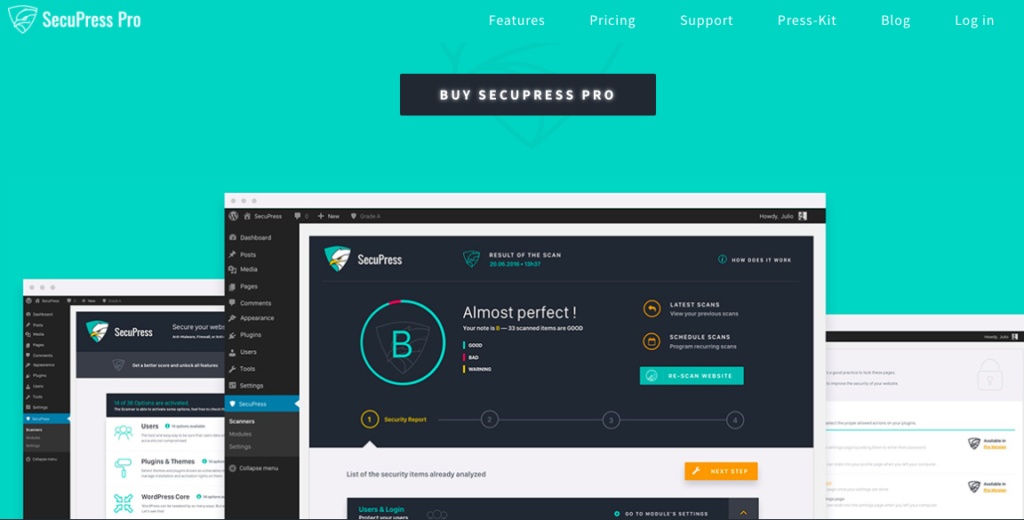
SecuPress protects a WordPress site from malware, blocks bots and suspicious IPs, and puts a genuinely clean interface on top. The free version already includes a firewall, anti-brute-force login protection, and IP blocking; the Pro version adds alerts, two-factor authentication, IP geolocation blocking, PHP malware scanning, and PDF reports. It was built by a well-known WordPress security expert, which shows in the details. As a French product, it is GDPR-native and backed by responsive support, which appeals to owners who want their security stack and their data handling to sit under European rules.
Key features:
- A broad set of automated security checks
- Custom login URL and brute-force protection
- PHP malware scanning (Pro) and IP geolocation blocking
- Two-factor authentication and PDF security reports
Pricing: free version for basic protection; Pro from €60 per year for a single site, with the per-site price dropping sharply as you add sites.
Pros
- One of the best interfaces of any security plugin
- Strong malware and bot protection with report generation
- Built by a recognized security expert
Cons
- The most advanced protections sit behind the Pro tier
- Still a per-site plugin, so it does not scale like a management platform
> Our single-site pick: if you run one site and want a standalone plugin you set up once and forget, SecuPress is our recommendation, with WP Cerber a strong alternative. For managing client sites at scale, the verdict is different, see WP Umbrella above and our security plugin alternative for agencies.
9. All-in-One Login
Best for: locking down the login page specifically, with 2FA.
The WordPress login page is the prime target for brute-force and credential-stuffing attacks, and All-in-One Login is built to defend exactly that. It offers a custom login URL, login-attempt limits per IP, detailed login activity, user and IP banning, and app-based multi-factor authentication, all through toggles rather than code snippets in functions.php. It does one job and does it cleanly, which also means you will want to pair it with a scanner or firewall for anything beyond the login page.
Key features:
- Custom login URL and login-attempt limits
- Detailed login activity log
- User and IP banning
- App-based multi-factor authentication (2FA)
Pricing: free version available; paid single-site plans from $29 per year (Basic), $49 per year (Professional), and $59 per year (Business).
Pros
- Clean, easy-to-use interface focused on login security
- Solid wp-admin protection and app-based 2FA
- Free version to start with
Cons
- Covers login security only, not malware or firewalling
- You will still need another layer for full protection
10. MalCare Security

Best for: cloud-based malware scanning with one-click cleanup.
Local scanners tend to choke on exactly the site that needs them most: one that is already infected or already slow. MalCare sidesteps that by running its malware scan in the cloud, on its servers rather than yours, which keeps it lightweight even mid-incident. It adds bot protection, a firewall, login protection with country-level IP blocking and captcha, one-click hardening, and a one-click malware removal tool that cleans a site before search engines flag it. It also alerts you when a site goes down.
Key features:
- Cloud-based malware scanner that runs off your server
- One-click malware removal
- Firewall with country-level IP blocking and captcha
- One-click hardening and bot protection
Pricing: free detection-only tier; paid plans from $99 per year (Protect), $299 per year (Repair), and $499 per year (Fortify), each for one site.
Pros
- Powerful cloud-based malware scanner with low performance impact
- One-click cleanup handled for you
- Broad set of protection features
Cons
- Uptime monitoring is less reliable than dedicated tools
- Refund policy is strict
See how it stacks up in our MalCare versus WP Umbrella comparison.
11. Jetpack Security

Best for: sites already living in the Automattic ecosystem that want backups and scanning.
If your sites already run on WordPress.com or lean on Jetpack, adding its Security bundle is the path of least resistance. It packages real-time backups, automated malware scanning, brute-force protection, Akismet spam filtering, a CDN, and site stats into one plugin most WordPress users already recognize. It integrates tightly with the WordPress.com account system and the Jetpack mobile app, which is convenient if you already live in that ecosystem and a bit of lock-in if you do not.
Key features:
- Real-time or daily backups
- Automated malware scanning
- Akismet spam filtering and brute-force protection
- CDN and site statistics
Pricing: free tier for Akismet-powered spam protection; the Security bundle (malware scanning and backups) is about $25 per month per site, billed yearly, with heavy first-year promotional pricing common.
Pros
- Adds essential features conveniently, from a trusted source
- The core Jetpack plugin is free, and Akismet spam filtering is excellent
Cons
- Feature sprawl makes the interface cluttered
- Users frequently report performance slowdowns
Our Jetpack versus WP Umbrella comparison covers the differences for multi-site owners.
12. WP Cerber Security

Best for: a single-site standalone plugin focused on anti-spam and login security.
Where All-in-One Login sticks to the login page, WP Cerber wraps that same login hardening in a wider anti-spam and malware layer. It blocks malicious activity before it reaches your data, and its anti-spam engine is a genuine strength, cutting comment and registration spam without a separate service. It supports Cloudflare integration, exporting security data, and scheduled scans, with a well-built interface and little apparent performance impact, which makes it a tidy choice for community and membership sites.
One important note: WP Cerber is no longer distributed through the wordpress.org plugin repository. It is now self-hosted through wpcerber.com, where it remains actively maintained in 2026, so downloads and updates come from the vendor rather than the WordPress directory.
Key features:
- Login-attempt limits and custom login URL
- Anti-spam for comments and contact forms
- Core-file integrity scanning
- Two-factor authentication and Cloudflare integration
Pricing: free version with local protection and automated spam protection for unlimited sites; Pro from $29 per quarter (or $99 per year) for a single site. The vendor’s tier structure can be confusing, so check current terms on the site.
Pros
- Effective login hardening and anti-spam, even on the free tier
- Clean, well-designed interface
- Little measurable impact on site performance
Cons
- No longer on the wordpress.org repository, so updates are self-hosted
- Pricing structure is easy to misread
13. Cloudflare
Best for: a network firewall and CDN layer in front of any site, whatever else you run.
Unlike everything else on this list, Cloudflare never touches your WordPress install. It sits in front of your site at the DNS level, filtering malicious traffic upstream, absorbing DDoS attacks, and serving your site faster through its CDN, all with zero load on your server. It complements a WordPress-level plugin rather than replacing it, since it cannot see inside WordPress the way an application firewall can. The practical move is to run Cloudflare in front and keep a WordPress-aware security layer behind it, so each catches what the other misses.
Key features:
- Network-level web application firewall (managed ruleset on Pro and above)
- DDoS mitigation
- Global CDN and caching
- DNS management and SSL
Pricing: Free plan at $0, but with only basic managed rules; the full WAF managed ruleset (including OWASP core protections) requires Pro at $20 per month (billed annually) or Business at $200 per month.
Pros
- Network-level firewall and DDoS protection with no server load
- Global CDN improves performance as a bonus
- A capable free plan for basic filtering and caching
Cons
- The meaningful WAF ruleset is gated behind Pro and above
- Cannot inspect WordPress internals, so it is a layer, not a complete solution
Final Thoughts
There is no single best WordPress security plugin, but there is a best fit for your situation.
If you own one site, pick a standalone plugin that matches your comfort level: SecuPress or Wordfence for full protection, All-in-One Login or WP Cerber if login hardening is your main concern, and Sucuri or MalCare if you want cleanup handled for you.
If you manage client sites, the calculus changes. Installing, licensing, and maintaining a security plugin on every site is its own overhead, and it still leaves updates, backups, monitoring, and reporting unsolved. WP Umbrella covers all of that from one platform, with Patchstack-powered vulnerability monitoring and virtual patching that do not slow sites down, which is why it is our pick for anyone running WordPress at scale.
And if you maintain client sites, package this work. Security monitoring is a core line item in WordPress care plans, and it is far easier to sell inside a plan than as an hourly favor. Start your free trial, no credit card required.
FAQs About WordPress Security Plugins
Most WordPress breaches come from vulnerable third-party extensions, weak passwords, abandoned plugins, or misconfigured hosting. Keeping everything updated and monitored matters more than any individual security feature.
For most sites, yes. The base platform covers vulnerability monitoring, safe updates, backups, uptime and error monitoring, security hardening, and two-factor authentication. The optional Security add-on adds a firewall with virtual patching and a daily remote malware scanner. Malware cleanup is available on demand, and a one-off Security Audit tells you whether a site was compromised.
Free plugins cover the basics, including basic scanning and file monitoring, but they lack deeper features like real-time firewall rules, scheduled scans, virtual patching, automated cleanup, and high-quality support. For sites that handle revenue, bookings, or customer data, a premium plugin or a management platform is strongly recommended.
Update it as soon as a patch is released. If you cannot update immediately (client approval, custom code, staging delays), virtual patching can block the known exploit while you wait.
It depends on the plugin’s architecture. Plugins that run deep scans locally, such as malware scanners or firewalls executed in PHP, can increase CPU usage and slow load times on shared hosting. Cloud-based or virtual-patching approaches, like WP Umbrella’s, tend to have far less performance impact. Always check resource usage before and after installation.
Hosting-level security is not the same as application-level protection. A good host filters malicious traffic and runs server firewalls, but it cannot see plugin vulnerabilities, outdated software, weak passwords, or file-level issues inside WordPress. A security plugin, or a management platform with security features, covers what hosting cannot.